// BEYOND CONVENTIONAL SECURITY

Cybersecurity from compliance to resilience.

We help organizations understand their cyber risk, make the right security decisions, and turn regulatory requirements into effective technical controls.

IT Security
OT Security
AI Security
Learn more
[ 01 ] / QYNTAR VALUES

WHY QYNTAR?

"Cybersecurity without technical expertise is just philosophy."

Anyone can make promises. We prefer evidence.

INDUSTRY PROMISE

ATTACKER MINDSET

QYNTAR EVIDENCE

FORMER PENTESTERS

Our technical judgment comes from people who have actually tested systems, not just studied how attacks work.

INDUSTRY PROMISE

BUSINESS UNDERSTANDING

QYNTAR EVIDENCE

FORMER CISO

Our cybersecurity leadership comes from real CISO experience in a highly regulated sector, where security decisions have to survive budgets, regulators, boards and operational reality.

INDUSTRY PROMISE

CERTIFIED EXPERTISE

QYNTAR EVIDENCE

HANDS-ON CERTIFIED TALENT

Most cybersecurity certifications test whether you can choose the right answer from a list. Ours require technical ability to be demonstrated hands-on.

INDUSTRY PROMISE

SECURE BY DESIGN

QYNTAR EVIDENCE

SECURITY BUILT INTO ENGINEERING

Security can’t be designed in by people who don’t speak engineering. Our engineers and security specialists work side by side to understand how software, embedded, OT and cyber-physical systems interact.

SERVICES

Your security partner, from audit readiness to attacking and defending the most critical systems.

[ 03 ] / Cybersecurity capability development

OFFSEC × QYNTAR
CYBER CAPABILITY

Hungary’s first and only official OffSec partner.

More than training. A measurable path from potential to proven capability.
>01 / HIRE

VALIDATE BEFORE YOU HIRE

Validate practical ability through hands-on technical assessment, not just interviews, CVs or certifications.

>02 / ASSESS

FIND THE CAPABILITY GAPS

Measure real technical capability, identify skill gaps and understand where development will have the greatest impact.

>03 / DEVELOP

BUILD HANDS-ON CAPABILITY

Develop offensive, defensive and broader cybersecurity skills through practical training, labs and certifications.

>04 / VERIFY

VERIFY WHAT YOUR TEAM CAN DO

Validate capability through practical assessments that require people to demonstrate what they can actually do in technical environments.

[ 04 ] / Industries

Industries

Security solutions for critical sectors facing continuously evolving threats.

qyntar://industries

Automotive Cybersecurity Services

Ensuring regulatory compliance and controlling the risks of software-defined vehicle platforms.

Modern vehicles are increasingly becoming complex, software-driven systems integrating hundreds of ECUs, cloud connectivity, and over-the-air updates. Development processes often focus on functionality and safety requirements, while cybersecurity risks are only addressed at later stages. Qyntar integrates cybersecurity analysis into model-based development environments, identifying potential attack surfaces already during system design. Our experts analyze vehicle architectures through attack scenarios and support development teams in embedding security requirements into engineering workflows. Our approach supports compliance with standards such as ISO/SAE 21434, UNECE R155/R156, and the security validation of model-based processes used in automotive software development.

Automotive cybersecurity
  • Support for ISO/SAE 21434 and UNECE R155 / R156 compliance
  • Analysis of attack surfaces across ECUs, vehicle networks, and OTA updates
  • Secure-by-design architecture and threat modeling integrated into development

Defense and Aerospace

Reducing project risk and meeting high security requirements in contractual environments.

Defense and aerospace systems are highly complex, long-lifecycle platforms in which digital, embedded, and cyber-physical components are tightly integrated. Security is often shaped by strong regulatory and documentation requirements, while analysis of realistic attack models remains limited. Qyntar applies a technical adversarial perspective to analyze complex system architectures, uncovering attack paths across IT, OT, and embedded environments. Model-based analytical methods allow security risks to be identified already during system design and integration. Our services support compliance with relevant industry requirements, including frameworks such as NIST 800-53, NIST 800-171, NATO and EU cybersecurity frameworks, as well as audit and compliance processes for safety-critical systems.

Aerospace and Defense industry cybersecurity
  • NIST 800-53 / 800-171-based controls and audit readiness
  • Identification of attack paths across IT, OT, and embedded systems
  • Supply chain security and third-party risk management

Energy and Utilities

Benefit: minimizing outages and strengthening the resilience of critical infrastructure.

Energy and utility systems increasingly rely on digital control systems, industrial networks, and remote management infrastructure. These environments often combine decades-old technologies with newly integrated digital components, resulting in complex and difficult-to-overview attack surfaces. Qyntar analyzes critical infrastructure architectures to identify potential attack paths between IT and OT systems, and helps organizations design security measures based on realistic threat models. Our approach supports compliance with standards and regulations such as NIS2, IEC 62443, and national and European cybersecurity requirements for critical infrastructure.

Energy and Utilities cybersecurity
  • Technical implementation support for IEC 62443 and NIS2 requirements
  • Analysis of attack surfaces across IT–OT boundaries and industrial networks
  • Incident response and operational continuity in critical systems

Pharmaceuticals and Healthcare

Benefit: protecting intellectual property, reducing the impact of outages, and accelerating approvals.

Healthcare and pharmaceutical systems increasingly depend on connected digital infrastructures, medical devices, and data-intensive platforms. The sector places particular emphasis on protecting patient data and ensuring continuous system availability, while devices and platforms often operate within complex supplier ecosystems. Qyntar identifies risks exploitable in real operating environments through technical analysis of architectures and integration points. The model-based approach supports the structured integration of security requirements into development and operational processes. Our services contribute to compliance with regulations and standards such as HIPAA, GDPR, IEC 62304 for medical systems, and related security requirements.

Pharma and Health industry cybersecurity
  • Support for GDPR, HIPAA, and medical device standards (IEC 62304)
  • Analysis of attack surfaces across medical systems and integrations
  • Reduction of system outage and data loss risk

Financial Services

Benefit: stronger return on investment through proactive risk reduction.

The financial sector operates with rapid digital innovation, cloud-based infrastructure, and the integration of new technologies such as artificial intelligence and decentralized systems. Fast development cycles and complex supplier chains can create significant risk, especially in the protection of critical business processes and sensitive data. Qyntar applies a technical adversarial perspective to analyze financial system architectures, identifying potential attack surfaces across cloud, application, and integration layers. Our experts help organizations ensure that security controls do not serve compliance alone, but are also effective against real threats. Our approach helps organizations align with regulatory frameworks such as DORA, PCI DSS, and international cybersecurity standards used in the financial sector.

Finance industry cybersecurity
  • Technical alignment with DORA, PCI DSS, and central bank regulatory requirements
  • Assessment of attack surfaces across cloud, APIs, and digital platforms
  • Management of security risks in AI and data platforms

AI & Emerging Technologies

Benefit: innovation without introducing uncontrolled risk.

New technologies are often adopted faster than they are understood. AI and LLM systems, autonomous agents, and other emerging platforms introduce attack surfaces that traditional security programs were never designed to cover, from prompt injection and data leakage to insecure integrations and unclear accountability. Qyntar applies a technical adversarial perspective to test how these systems behave under real attack, not just how they are described in documentation. Our experts help organizations ensure that governance and controls are backed by technical evidence, and that innovation moves forward with risk that is understood and managed.

Our approach helps organizations align with emerging regulation and standards such as the EU AI Act, ISO/IEC 42001, and OWASP guidance for LLM applications.

Pharma and Health industry cybersecurity
  • Adversarial testing of AI systems, LLM applications, and AI agents
  • Assessment of attack surfaces across models, data pipelines, and integrations
  • Technical grounding for AI governance and regulatory readiness
[ 05 ] / ABOUT

QYNTAR

Qyntar is a Budapest-based cybersecurity and security engineering company serving organizations across Europe. We secure complex digital systems, from IT infrastructure and cloud to industrial control systems (OT/ICS), AI/LLM applications, and connected products, and we build cybersecurity capability inside the organizations we work with.

What differentiates us is the experience behind our decisions. We do not rely on paper-only expertise: our people have attacked systems, led security programs where accountability was real, and demonstrated their skills hands-on.

For complex and mission-critical environments, our cybersecurity specialists work alongside engineers to analyze and secure products, architectures, and interconnected systems across IT, OT, embedded technologies, AI, and cyber-physical environments.

Who we work with

We focus on environments where a security failure has serious consequences: critical infrastructure, healthcare, financial services, automotive, defense and aerospace.

We also support technology companies, manufacturers and growing businesses outside these sectors that handle sensitive data, run critical processes or face regulatory pressure such as NIS2, DORA, IEC 62443 and Cyber Resilience Act.

The people responsible for your security

Behind every engagement stand practitioners who have broken real systems, carried C-level security accountability and researched security problems at doctoral depth.

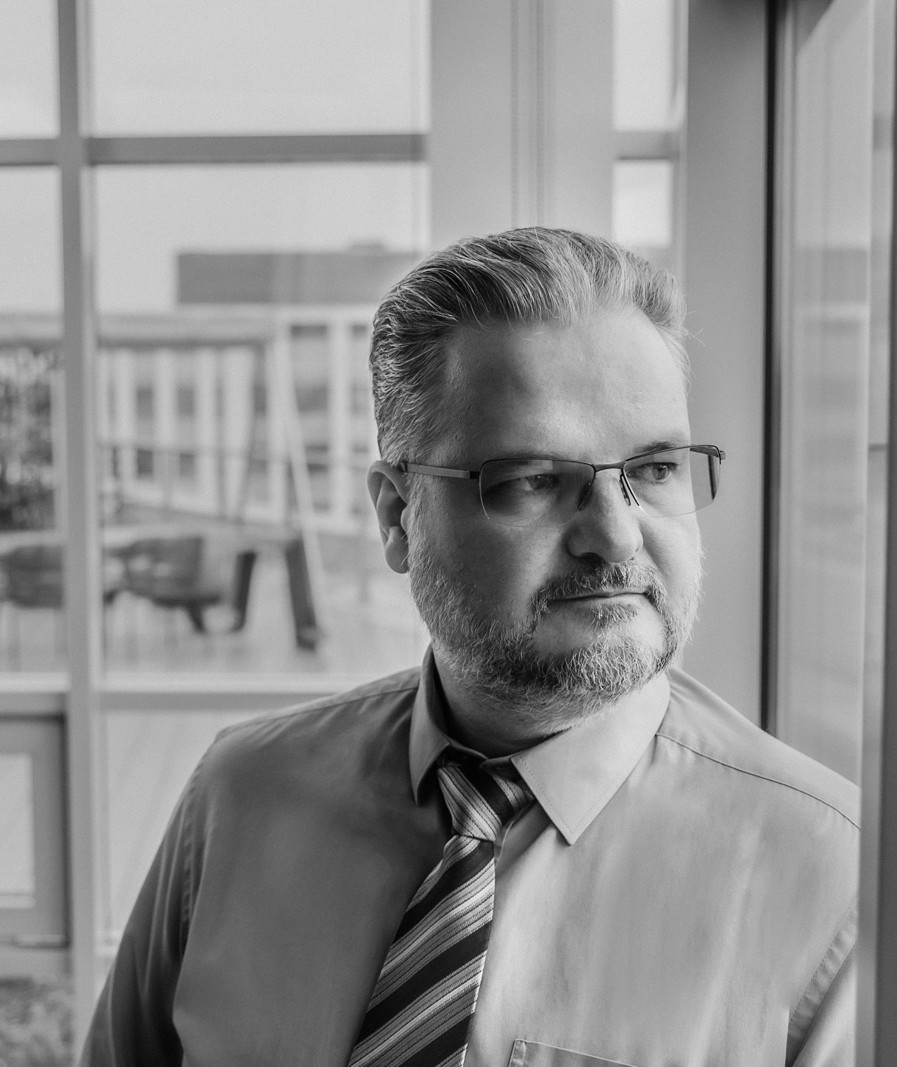
Peter Bolesza
// FOUNDER

Bolesza Péter

Co-Founder & CEO

Peter has a broad background in engineering, technology business development, and complex industrial settings. His background bridges cybersecurity, engineering, and business risk, ensuring Qyntar’s work is aligned with how critical systems are actually designed, operated, and used.

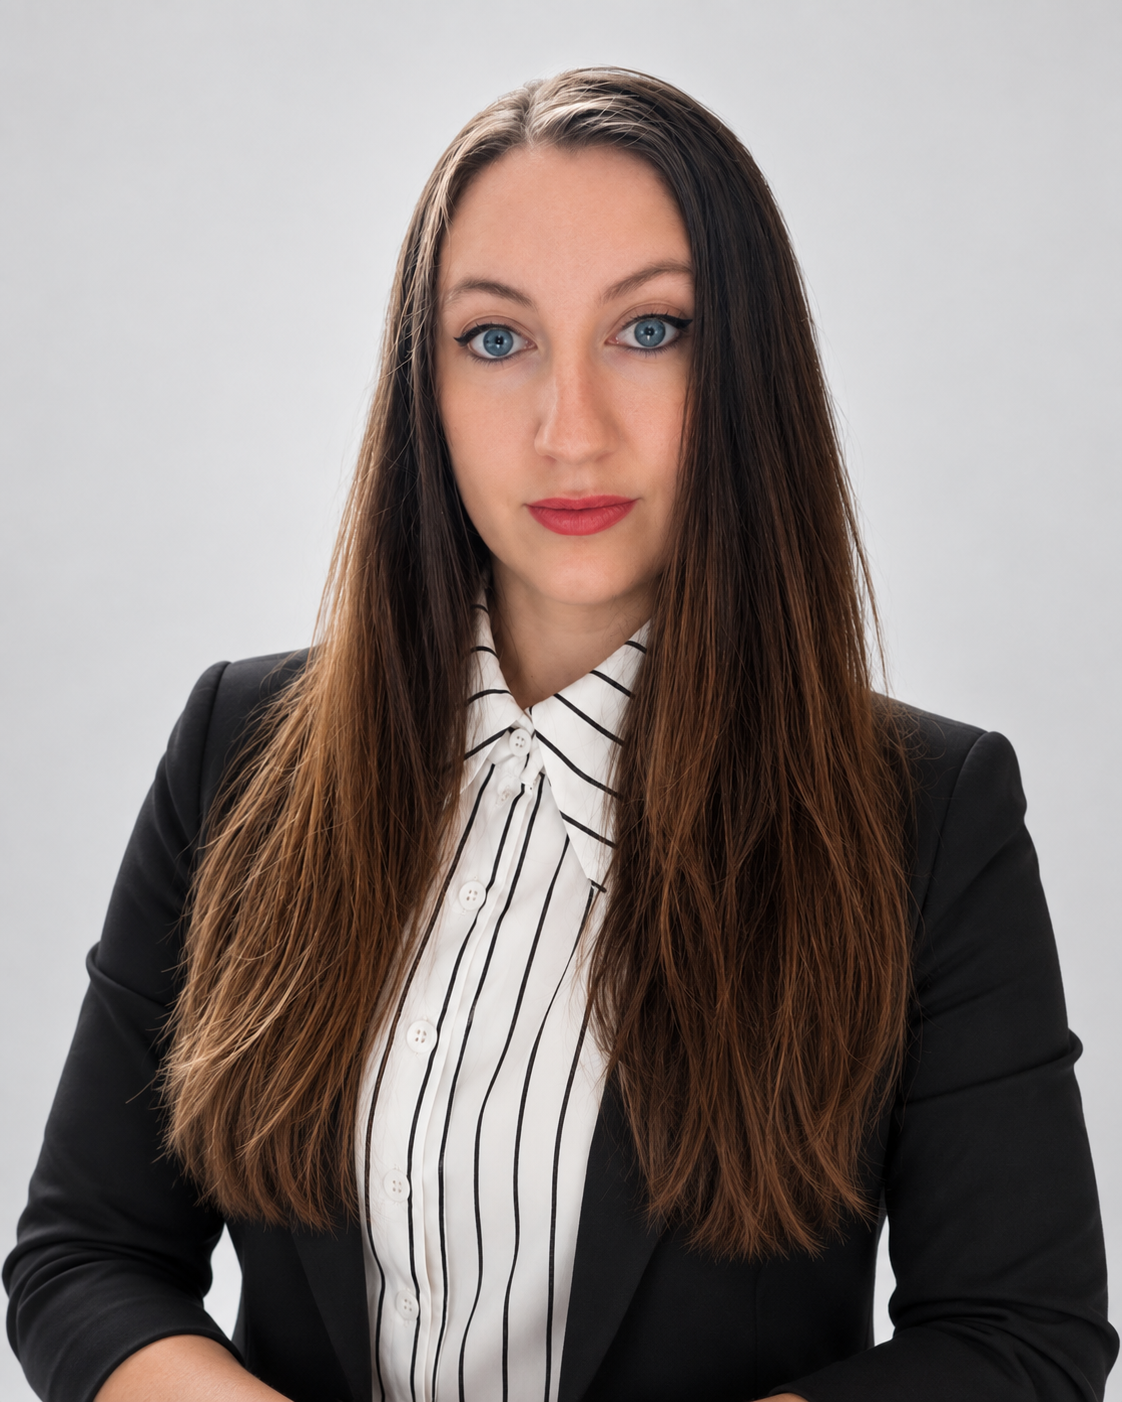
Szandra Steinle
// FOUNDER

Steinle Szandra

Co-Founder & CTO

Szandra has 15 years of cybersecurity experience, spanning penetration testing, offensive security, enterprise security leadership and AI security. She spent six years in a multinational environment, including serving as a Local CISO, and is currently pursuing a PhD at ELTE’s Doctoral School of Informatics, focusing on AI security.

CERTIFICATIONS

OSCP certification OSWE certification OSEP certification OSED certification OSAI certification CEH certification CHFI certification ECIH certification
[ + ] / CONTACT

Contact

E-mail

Tell us about your security challenge.

From a specific technical issue to a complex security project, we can help you find the way forward.

Show email address
info qyntar com